Cryptographic Inventory: The First Step Most Organisations Have Not Taken

Digital transformation / Post Quantum readiness

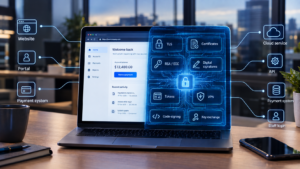
Most organisations cannot answer a simple question: Where do we use cryptography? That is not because they are careless. It is because cryptography is designed to disappear into the background.   When it works, nobody thinks about it. A customer logs into a portal. A payment system connects to a bank. A staff member opens a… Continue reading Cryptographic Inventory: The First Step Most Organisations Have Not Taken
Read More

What Customer Trust Will Look Like in the Post-Quantum Era?

Digital transformation / Post Quantum readiness

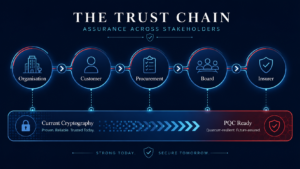
For years, organisations have demonstrated cyber trust through familiar evidence: security certifications, penetration tests, privacy policies, audit reports, incident-response plans and contractual commitments.   Post-quantum cryptography is about to add another category.   Not immediately. And not because customers will suddenly expect every supplier to have replaced every cryptographic system.   The change is more… Continue reading What Customer Trust Will Look Like in the Post-Quantum Era?

Read More

How to Talk to Your Board About Post – Quantum Risk Without Creating Panic

Digital transformation / Post Quantum readiness

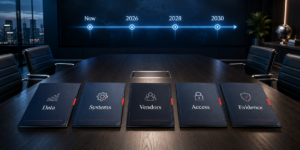
Post-quantum risk is difficult to brief at board level.   Handled badly, it sounds either too technical or too speculative. Too technical, and directors disengage. Too speculative, and the message sounds like fear-based cyber marketing. Too urgent, and leadership may ask why the organisation is not already acting. Too relaxed, and the issue gets pushed… Continue reading How to Talk to Your Board About Post – Quantum Risk Without Creating Panic

Read More