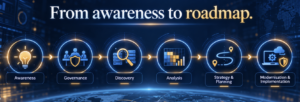
From Awareness to Roadmap: What a Practical PQC Readiness Program Looks Like

Digital transformation / Post Quantum readiness

Most organisations now understand that post-quantum cryptography is coming.   That awareness is useful. But awareness alone does not reduce risk.   The real question is what happens next.   A leadership team may know that quantum-vulnerable cryptography matters. A CIO may know that systems, vendors, certificates, identity tools, APIs and legacy applications could be… Continue reading From Awareness to Roadmap: What a Practical PQC Readiness Program Looks Like
Read More

The PQC Questions Every Organisation Should Ask Its Vendors

Digital transformation / Post Quantum readiness

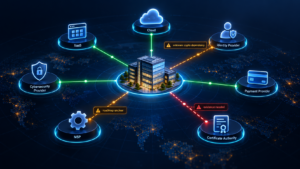
Most organisations will not complete post-quantum transition alone.   They will depend on: Vendors. Cloud providers. SaaS platforms. Identity providers. Payment providers. Software suppliers. Managed service providers. Cybersecurity vendors. Certificate authorities. Hardware and firmware suppliers. Legacy product owners.   That makes vendor readiness one of the most important parts of PQC planning.   It also… Continue reading The PQC Questions Every Organisation Should Ask Its Vendors

Read More

The Hidden Risk in Legacy Systems During PQC Transition

Digital transformation / Post Quantum readiness

Legacy systems have a strange habit. They sit quietly in the corner of the organisation, doing something important enough that nobody wants to touch them. They run the old portal.They hold the old records.They connect to the old vendor.They support the old workflow. They generate the report everyone still needs.They authenticate users in a way… Continue reading The Hidden Risk in Legacy Systems During PQC Transition

Read More