Why Long-Life Data Changes the PQC Risk Equation

Digital transformation / Post Quantum readiness

Some information becomes less sensitive with time. Other information can damage lives, businesses and reputations decades after it was created.   A password can be changed. A payment card can be replaced. A temporary commercial offer eventually expires.   But what about a client’s legal history? A patient’s medical records? Personal identity documents? Confidential settlement… Continue reading Why Long-Life Data Changes the PQC Risk Equation
Read More

From Awareness to Roadmap: What a Practical PQC Readiness Program Looks Like

Digital transformation / Post Quantum readiness

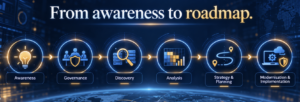
Most organisations now understand that post-quantum cryptography is coming.   That awareness is useful. But awareness alone does not reduce risk.   The real question is what happens next.   A leadership team may know that quantum-vulnerable cryptography matters. A CIO may know that systems, vendors, certificates, identity tools, APIs and legacy applications could be… Continue reading From Awareness to Roadmap: What a Practical PQC Readiness Program Looks Like

Read More

The PQC Questions Every Organisation Should Ask Its Vendors

Digital transformation / Post Quantum readiness

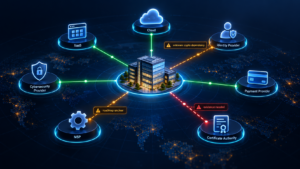
Most organisations will not complete post-quantum transition alone.   They will depend on: Vendors. Cloud providers. SaaS platforms. Identity providers. Payment providers. Software suppliers. Managed service providers. Cybersecurity vendors. Certificate authorities. Hardware and firmware suppliers. Legacy product owners.   That makes vendor readiness one of the most important parts of PQC planning.   It also… Continue reading The PQC Questions Every Organisation Should Ask Its Vendors

Read More